Wilhelm Maritz
  • Home
  • About
  • Skills
  • Projects
  • Posts
  • Dark Theme
    Light Theme Dark Theme System Theme
  • Tags
  • Algorithms
  • Architecture
  • Automation
  • Backups
  • Batch
  • Btrfs
  • Caching
  • Case-Study
  • Cloudflare
  • Code-Review
  • Cryptography
  • Debugging
  • Deployment
  • Docker
  • Documentation
  • Expressions
  • Firebase
  • Flask
  • Game-Design
  • Git
  • Graphics
  • Hardware
  • Homelab
  • Hugo
  • Hyprland
  • Incidents
  • Javascript
  • Jinja
  • Johnny-Decimal
  • Knowledge-Management
  • Linux
  • Low-Code
  • Markdown
  • Mentoring
  • Monitoring
  • Obsidian
  • Omarchy
  • Onedrive
  • Opinion
  • Organisation
  • Parsing
  • Physics
  • Power-Automate
  • Process
  • Pygame
  • Python
  • Raid
  • Railway
  • Safari
  • Security
  • Self-Hosting
  • Sqlite
  • Ssh
  • Static-Sites
  • Tailscale
  • Timezones
  • Tooling
  • Windows
  • Wsl
  • Zettelkasten
  • Zimaos
Hero Image
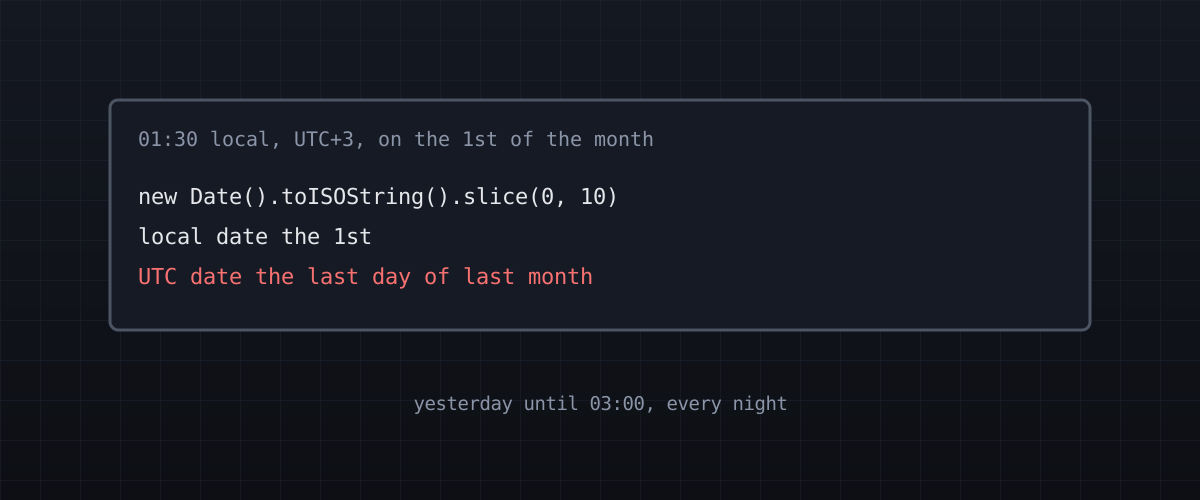
The date that was yesterday until 3am

This line looks harmless: const today = new Date().toISOString().slice(0, 10); toISOString() gives the UTC date. I live in UTC+3, so from midnight until 03:00 every night that line names yesterday, and on the first of a month it names the previous month. An app I maintain did it in three places: the today marker on a calendar, and a gate on the admin page that decides whether the month you’re editing is already in the past, twice. Nobody had noticed, because nobody uses a rostering app at 2am. Except the schedulers, who work nights. It surfaced in the review of the change that moved the app’s scripts out of its templates, as an old bug in code that change had only relocated.
Friday, September 11, 2026 | 3 minutes Read
Hero Image
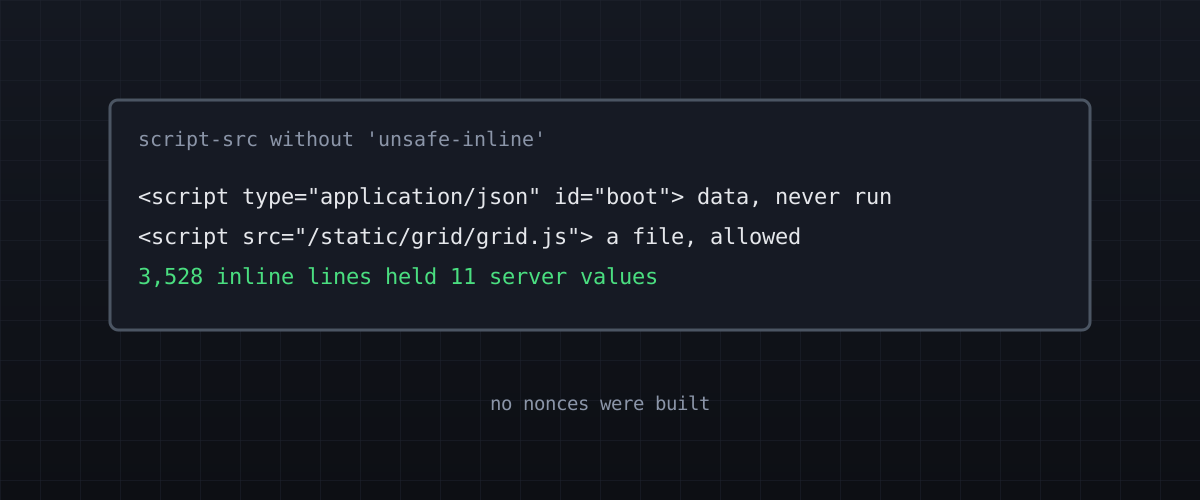
Enforcing a Content-Security-Policy without nonces

An app I maintain kept its JavaScript inline. The main page’s template was 3,979 lines, and 3,528 of them were one <script> block. Eight other pages were the same shape, around 6,500 lines in all. That rules out a strict Content-Security-Policy. A policy that blocks injected scripts has to drop 'unsafe-inline' from script-src, and then every one of those blocks stops running. The usual answer is a nonce per request on every script tag. I didn’t build that.

Thursday, September 10, 2026 | 3 minutes Read
Hero Image
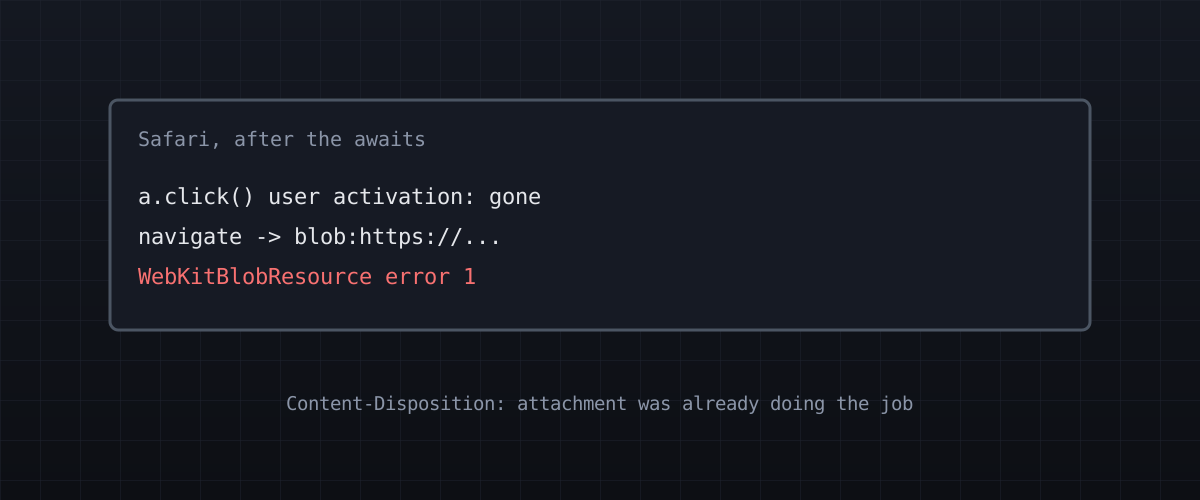
Safari could not download the file

A Mac user clicked Export in an app I maintain and got this instead of a spreadsheet: WebKitBlobResource error 1 The pattern that broke The download code was the pattern you find everywhere: fetch the file, turn it into a blob, point an invisible link at it, click the link, tidy up. In outline: async function download(url, name) { const res = await fetch(url); const blob = await res.blob(); const a = document.createElement("a"); a.href = URL.createObjectURL(blob); a.download = name; a.click(); URL.revokeObjectURL(a.href); } The app had four hand-rolled copies of it.

Wednesday, September 2, 2026 | 2 minutes Read
Navigation
  • About
  • Skills
  • Projects
Contact me:
  • [email protected]
  • B3ardBr0
  • Wilhelm Maritz

Toha Theme Logo Toha
© 2026 Wilhelm Maritz
Powered by Hugo Logo